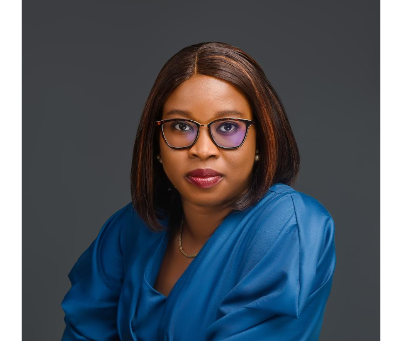
Onyinye Lydia Abuo has called for a shift from policy-driven data protection to practical, everyday systems that help organisations manage data risks and protect personal information at every level of their operations.
Abuo, who focuses on enterprise-scale data risk and privacy frameworks, said organisations must move beyond drafting privacy policies and signing compliance documents to ensuring that data protection principles are reflected in daily business processes and supported by verifiable evidence.
According to her, an effective framework rests on three pillars: policy, process and proof.
“A privacy policy is the easy part. Anyone can draft one in a week,” she said, noting that the real test comes when an employee is about to share customer information with the wrong person under pressure.
She argued that such everyday situations reveal whether an organisation’s data protection framework works in practice or exists merely on paper.
Abuo explained that the challenge becomes more complex as organisations expand, with multiple departments, branches, systems and suppliers operating under the same rules but often following different work practices.
While a small team might rely on memory and goodwill to protect personal information, she said, large organisations require clear procedures and consistent controls because a single failure can expose the business to reputational damage and regulatory scrutiny.
She also pointed to the evolution of Nigeria’s data protection landscape, from the Nigeria Data Protection Regulation (NDPR) to the Nigeria Data Protection Act 2023 (NDPA) and the establishment of a dedicated regulatory authority.
However, she warned that issuing policies and obtaining signed acknowledgements did not necessarily mean that business practices had changed.
“The question is: ‘So what changed in the business when the change happened?’” she said.
Policy Must Be Clear and Practical
Abuo said privacy policies should be concise, clear and tailored to the responsibilities of the people expected to implement them.
She cautioned against filling internal documents with legal language that employees might struggle to understand, arguing that policies should provide practical guidance rather than simply reproduce statutory provisions.
Her preferred test, she explained, is whether a new employee can understand and follow a policy without needing a lawyer to interpret it.
Embedding Privacy in Daily Processes
She identified process as a major weakness in many data protection frameworks, stressing that organisations cannot rely solely on employees’ goodwill to safeguard personal information.
Instead, privacy requirements should be incorporated into existing workflows, making compliance part of how work is routinely performed.
This includes maintaining a data inventory showing what personal information an organisation holds and where it is stored, conducting risk assessments for new projects involving personal data, and integrating those assessments into project planning from the outset.
Other essential measures, she said, include assessing suppliers before entering into contracts, establishing retention schedules for the routine deletion of data that is no longer required, and developing incident-response procedures that employees regularly practise.
She stressed that organisations must prepare for data breaches before they occur, particularly because regulatory notification obligations can impose tight deadlines.
Evidence Must Support Compliance Claims
Abuo said organisations must also be able to demonstrate that their controls exist and function effectively, rather than merely claiming to be compliant.
She identified completed risk assessments, dated access reviews, role-specific training records and evidence of incident-response exercises as examples of proof that should emerge from routine operations.
According to her, having to scramble for documentation whenever an auditor or regulator requests it may indicate that controls are not adequately embedded in the organisation.
She also advocated concise reporting to senior management, focusing on indicators such as unresolved high-risk issues, overdue reviews, incidents and near-misses.
She warned that reports must disclose when figures are incomplete or unreliable, arguing that misleading risk information could be more damaging than an honest acknowledgement of missing data.
Near-miss reporting, she added, is particularly important because it allows organisations to identify weaknesses before they result in serious incidents.
An organisation that records only major failures, she argued, loses opportunities to learn from smaller warning signs, such as an email sent to the wrong recipient.
Training Must Reflect Employees’ Roles
On staff training, Abuo questioned the effectiveness of annual awareness sessions that are too lengthy or disconnected from employees’ daily responsibilities.
She said training should reflect the specific risks workers encounter in their roles, including how customer-service agents handle information over the phone, how finance officers manage email communications and how developers use personal data in test environments.
She advocated short, practical and repeated sessions designed around real workplace situations, rather than relying on a single lengthy lecture each year.
Independence and Continuous Review
Abuo acknowledged that organisations face practical obstacles, including legacy systems that were not designed with privacy in mind, paper-based records, staff rotations that carry existing habits between departments, and business units that may regard compliance as an obstacle to meeting targets.
She said data protection officers must be positioned to help the business manage risks without becoming either rubber stamps or unnecessary bottlenecks.
Their independence and reporting lines are also critical, she argued, insisting that they should have direct access to senior management or the board without intermediaries filtering their concerns.
Otherwise, she warned, data protection risks could once again be reduced to paperwork rather than addressed in practice.
Abuo maintained that no privacy framework should be considered permanently complete because laws, products, business operations and suppliers change over time.
She recommended scheduled reviews, alongside additional assessments whenever new regulations or projects emerge, to ensure that controls remain effective.
For her, the real measure of success is a workplace where employees know how to handle personal information correctly without having to consult a policy document every time.
In a typical workplace scenario, she explained, an employee preparing to email a file containing customer information should encounter the appropriate warning, have access to a simple guide and know where to seek help.
For Abuo, that is what an effective data protection framework looks like: not a document gathering dust on a shelf, but a practical system that works when people need it.
Disclaimer
Comments expressed here do not reflect the opinions of Vanguard newspapers or any employee thereof.