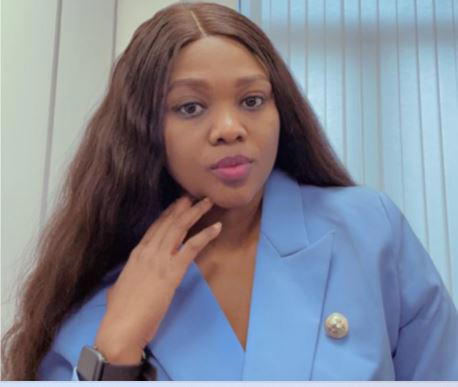
Ruth Itua
By Elizabeth Osayande
In an age where cybercrime is increasingly evolving, Nigerian businesses are being urged to bolster their defences against modern phishing attacks through comprehensive employee training. Ruth Itua, a seasoned security operations analyst and vulnerability manager with four years of experience, emphasises that “the most potent defence for Nigerian organisations may not be the latest firewall or intrusion detection tool; it may be people.”
With a master’s degree in Applied Artificial Intelligence and Data Analytics, Itua works closely with managed security service providers, focusing on minimising human-driven security risks. She has witnessed firsthand how cyber attackers are honing their craft to exploit human vulnerabilities, declaring, “Phishing remains the easiest and most reliable entry point for criminals.”
Modern phishing campaigns are not only targeted but also personalised and psychologically nuanced, making it vital for employees to recognise the signs. “Fraudsters now harness publicly available data from social media profiles and corporate websites to craft emails that feel familiar and legitimate,” Itua explains. This level of sophistication means that even savvy staff members can fall victim, particularly when attackers impersonate internal communications using compromised accounts or reference real company projects.
The introduction of multi-factor authentication, MFA offered some respite for organisations, but Ruth cautions that attackers have quickly adapted. “We’ve seen fake MFA prompts, social engineering calls, and even QR-based phishing pages emerge,” she warns. “These messages can easily mimic the tools that employees use every day.”
The ramifications of these attacks are becoming increasingly evident, with Nigerian organisations facing a surge in email compromises, fake payment instructions, and credential theft. “The problem is no longer a lack of technology; it is the human factor,” Ruth asserts, urging businesses to recognise the vital role of employee training in cybersecurity measures.
To defend against these evolving threats, the data analyst advocates for regular, realistic, and engaging training programmes. “Penetration testing is also essential to see how employees interact with scenario-based attacks,” she notes. “The organisations that treat their staff as active defenders instead of weak links will stay ahead.”
In conclusion, while technology will always play a critical role in cybersecurity, Itua emphasises that it can not replace human judgment. “With consistent training and practical simulations, employees can become an early warning system instead of an open door,” she says, underscoring the necessity of investing in human capital for a resilient defence against cyber threats.
Disclaimer
Comments expressed here do not reflect the opinions of Vanguard newspapers or any employee thereof.